Researchers Uncover 20,000 Malicious Cloudflare Pages Domains Used in Tech Support Scams
Infoblox found over 20,000 Cloudflare Pages domains used by Help TDS for Microsoft tech-support scams.
Infoblox says Help TDS, a traffic-distribution system it links with high confidence to the Russian-language Hotejka affiliate program and the older ROI777 operation, has used more than 20,000 malicious Cloudflare Pages domains for technical-support scams. Affiliates send victims from compromised sites, malvertising, spam, and social media; the system fingerprints browsers and location, then shows fake Microsoft lock screens that pressure users to call a support number. In a June 2026 test call, an operator impersonating Microsoft support told researchers to install UltraViewer. The chain also uses a malicious WordPress plugin, woocommerce_inputs, previously tied by GoDaddy to more than 10,000 compromised sites. This is abuse of trusted hosting, not a disclosed Cloudflare vulnerability.
- Infoblox tracked more than 20,000 scam-related Cloudflare Pages domains over six months.
- Help TDS is tied to Hotejka, assessed as a rebrand of ROI777 dating to at least 2017.
- Victims see fake Microsoft lock screens and are pushed to install UltraViewer.
- Delivery uses compromised WordPress sites, malvertising, spam, social media, and a Telegram bot.
- About 300 new pages.dev domains were announced daily; exposure later fell toward 0.5%.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | hotcname.help | omain Primary affiliate site hotns[.]rest Domain Nameserver hotcname[.]help Domain CNAME used by affiliates for DNS redirection usa.o |
| domain | hotejka.ink | anges. IOCs Domain / IP Address Type Role / Hosting Details hotejka[.]ink Domain Primary affiliate site hotns[.]rest Domain Nameser |
| domain | hotns.rest | Hosting Details hotejka[.]ink Domain Primary affiliate site hotns[.]rest Domain Nameserver hotcname[.]help Domain CNAME used by af |
| domain | on1xvpn.com | elp Domain CNAME used by affiliates for DNS redirection usa.on1xvpn[.]com Subdomain Hotejka On1x VPN endpoint 62.113.117[.]248 IPv4 |
| domain | pages.dev | ce software. Since April 2026, Help TDS has used disposable pages[.]dev infrastructure, announcing approximately 300 new domains |
| domain | serv.host | s VDSINA VDS Hosting — AS48282 91.196.33[.]144 IPv4 address SERV.HOST GROUP LTD — AS207957 Note: IP addresses and domains are int |
Full article720 words · extracted from gbhackers.com · click to collapse
More than 20,000 malicious Cloudflare Pages subdomains used by Help TDS, a longstanding traffic distribution system that funnels victims into fraudulent technical support call centers.
Researchers assess with high confidence that Hotejka, a Russian-language affiliate program, operates Help TDS and represents a rebrand of ROI777.
Historical DNS records, shared infrastructure, persistent affiliate identifiers, and consistent command-and-control mechanisms connect the entities.
The operation dates to at least April 2017, demonstrating unusual longevity despite repeated public exposure.
Affiliates deliver visitors through specially crafted URLs distributed through compromised websites, malvertising, spam, social media, and even a Telegram bot advertised as a free AI assistant.
Help TDS evaluates browser characteristics and geographic location before selecting a destination. Traffic unsuitable for technical support scams is resold through other affiliate platforms.
Selected victims encounter a fabricated update notification followed by warnings claiming Microsoft has disabled their computer.
Full-screen manipulation, exit prevention, flashing alerts, alarms, and recorded instructions create the impression of a system lock, pressuring users to call a displayed support number.
During a June 2026 investigation, Infoblox researchers contacted one advertised number. An operator impersonating Microsoft support instructed them to clear the browser lock, then download UltraViewer.
The call ended after researchers questioned the installation.
No subsequent compromise was demonstrated, but granting access through the legitimate remote desktop application would create an opportunity for further abuse.
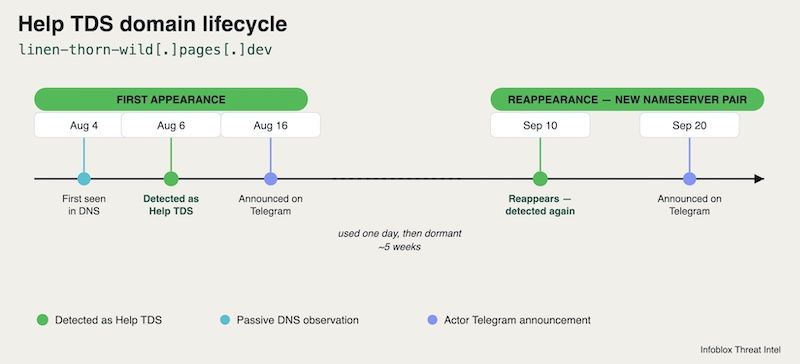
Infoblox Researchers observed that, the operation combines compromised websites, browser fingerprinting, aggressive scareware, and legitimate remote desktop software to turn ordinary browsing sessions into opportunities for unauthorized access.
20,000 Malicious Cloudflare Pages
The delivery chain builds on earlier WordPress compromises. GoDaddy previously documented the malicious woocommerce_inputs plugin, which retrieves redirect destinations, filters visitors, harvests account information, and supports automatic updates.
Its researchers estimated that the campaign affected more than 10,000 websites; the plugin is unrelated to legitimate WooCommerce software.
Since April 2026, Help TDS has used disposable pages[.]dev infrastructure, announcing approximately 300 new domains daily through Telegram.
The post reads “We accept ANY traffic: email SPAM, Facebook, Taboola, shells, WP admin panels, doorway pages, etc.”
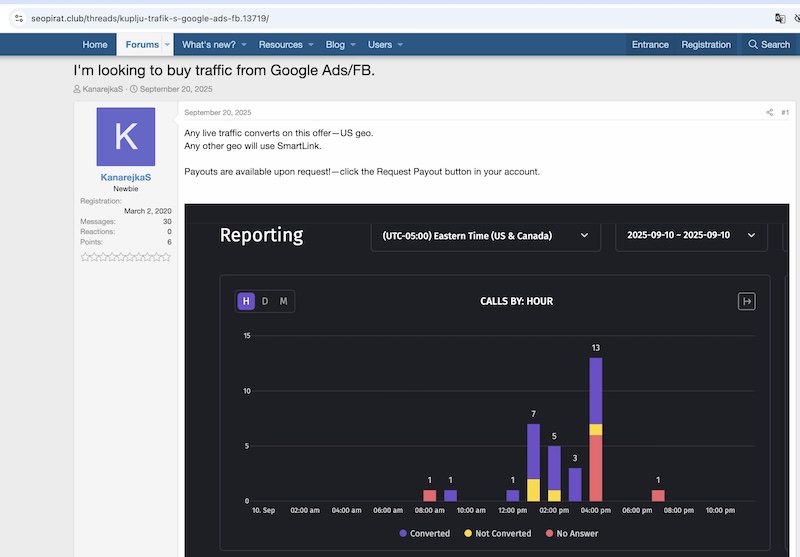
Infoblox observed more than 20,000 scam-related domains over six months, alongside roughly 10,000 additional domains associated with suspected phishing or decoy activity. These categories should not be interpreted as 30,000 confirmed scam destinations.
The actor uses multiple domain generation algorithms to blend into a platform where Infoblox typically observes more than 125,000 new subdomains daily.
Some domains display benign-looking advertisements or financial application lures during direct inspection, complicating classification.
This reflects broader abuse of trusted hosting rather than a disclosed Cloudflare vulnerability.
Fortra previously documented attackers exploiting Cloudflare Pages for phishing redirects and credential theft, benefiting from inexpensive deployment, HTTPS, and reliable infrastructure.
Infoblox reverse-engineered naming patterns and developed detectors that identify likely infrastructure approximately seven days before operational use.
Through mid-September, researchers detected more than 16,000 domains subsequently used by Help TDS. Reported customer exposure declined from daily peaks approaching 4% to around 0.5%; those figures measure exposure, not confirmed infections.
The historical connection is significant: a 2018 Operation Prowli investigation already identified ROI777 monetizing traffic from compromised websites, including redirects to technical support scams.
For defenders, the findings reinforce the importance of auditing WordPress plugins, protecting administrator accounts, and monitoring unauthorized redirects.
GoDaddy specifically recommends multifactor authentication, plugin audits, and monitoring suspicious scheduled tasks, measures that address the compromised website entry points sustaining this ecosystem across successive infrastructure changes.
IOCs
| Domain / IP Address | Type | Role / Hosting Details |
|---|---|---|
| hotejka[.]ink | Domain | Primary affiliate site |
| hotns[.]rest | Domain | Nameserver |
| hotcname[.]help | Domain | CNAME used by affiliates for DNS redirection |
| usa.on1xvpn[.]com | Subdomain | Hotejka On1x VPN endpoint |
| 62.113.117[.]248 | IPv4 address | VDSINA VDS Hosting — AS48282 |
| 91.196.33[.]144 | IPv4 address | SERV.HOST GROUP LTD — AS207957 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.